SHA1:
- 2ce5f1de24e5ac0d394ce12919343be2bcf9832f
A multi-purpose backdoor for Microsoft Windows that was distributed in social networks as a free license key for commercial anti-virus products. It is a packed tool called Njrat 0.7 Golden By Hassan Amiri (BackDoor.NJRat.1013). The Trojan contains a keylogger as one of the components.
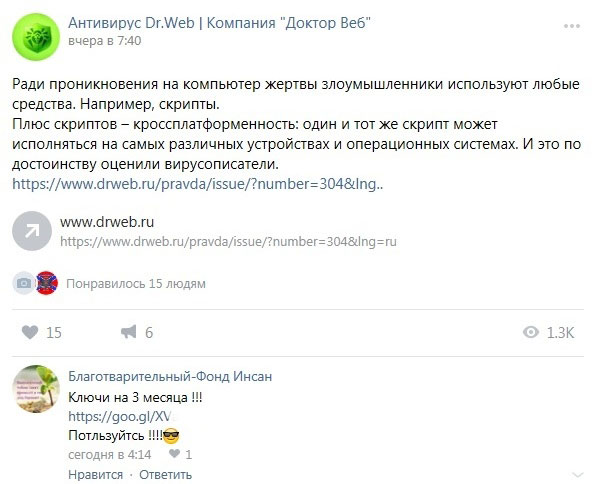
Once the Trojan is launched, it establishes a connection with the command and control (C&C) server and uploads the following data:
- Serial number of a hard drive;
- Operating system version;
- Operating system bitness;
- Identify the web camera connected to the computer;
- Computer name;
- User name;
- Version of the installed Service Pack;
- Version of the installed anti-virus.
The Trojan can execute the following commands of cybercriminals:
- Replace the Windows Desktop wallpaper;
- Turn off or restart the computer;
- Output a system message with the specified text on the screen;
- Swap the functions of mouse keys;
- Play a specific phrase using a voice synthesizer and speakers;
- Hide and then restore the Windows taskbar;
- Open or close the optical disc drive;
- Turn a display on and off;
- Open the specified link in a browser;
- Read, install or remove the specified value of the system registry;
- Receive a screenshot and send it to the C&C server;
- Download and launch the specified executable file;
- Send data collected by the keylogger to the C&C server;
- Refresh or remove the Trojan’s executable file;
At the command of cybercriminals it can display frightening SWF videos.